Daten-Sicherheit und Datenschutzbeauftragte aus Köln – English
Datenschutzbeauftragter in Köln

Focus on your business in Germany.
We take care of Data Protection and Information Security.

GDPR, ISO 27001 and NIS2 – practical, effective and without unnecessary bureaucracy.

Tulos IT-Sicherheit und Datenschutz aus Köln

4.9 out of 5 stars based on 36 google reviews.

Meet German and EU compliance requirements

Reduce data protection, cyber and liability risks

Meet customer, auditor and insurer requirements

Over 20 years of enterprise experience. Mid-sized business pragmatism.

We understand the requirements of international companies operating in Germany – as well as those of German and European regulators, customers, auditors and insurers – and turn them into practical, cost-effective solutions.

Datenschutzbeauftragter Köln

Why Companies Choose Tulos

We take care of Data Protection and Information Security – reducing risks, ensuring compliance and minimizing the effort required from your organization.

Ensure Compliance

Meet GDPR, ISO 27001 and NIS2 requirements in Germany and across the EU.

Reduce Risks

Reduce cyber, data protection and liability risks.

Reduce Internal Effort

Clear responsibilities. Efficient processes. Less bureaucracy.

We identify the risks, define the necessary measures and support their practical implementation.

Roderich Pilars de Pilar, Founder of Tulos Consulting GmbH

Our Solutions

Data Protection and Information Security from a Single Source

Certified Data Protection Officers and ISO 27001 Lead Auditors with extensive experience in German and international business environments.

We combine Data Protection and Information Security to reduce risks, meet regulatory and customer requirements and keep compliance manageable for your organization.

Talk to our Data Protection and Information Security experts.
Your initial consultation is free.

About Tulos

Who We Are and What We Do

Tulos stands for practical results. We help companies operating in Germany meet Data Protection and Information Security requirements without creating unnecessary complexity or bureaucracy.

We understand both business processes and IT systems. This enables us to identify risks across your organization and technology – and implement measures that work in day-to-day business.

Our ISO 27001 Lead Auditors and Information Security experts support organizations with ISMS implementation, risk management, audit readiness, NIS2 requirements and External CISO services.

Tulos provides employee training in the areas of data protection (GDPR) and information security. The secure handling of confidential data is one of the most important measures for reducing risks.

We work according to measurable standards, including ISO 27001, BSI, and NIS2.

Equal Opportunities Statement

Equal opportunities are a matter of course – regardless of origin, sexual identity, gender, age, or religion.

At Tulos Consulting, inclusion, diversity, and tolerance are among the company’s core values. Terms referring to persons on our website and in print materials apply equally to all genders unless explicitly stated otherwise.

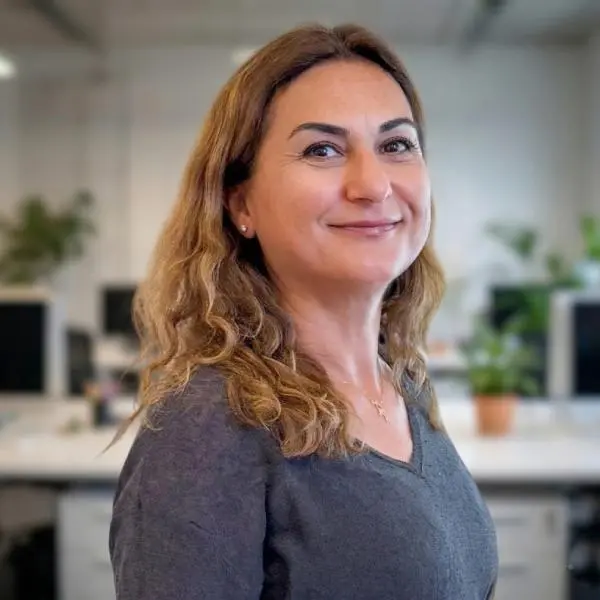
Roderich Pilars de Pilar, Datenschutzbeauftragter
Roderich Pilars de Pilar

Founder, Tulos Consulting GmbH

Nalan Erol
Nalan Erol

Nalan Erol Dipl.-Computer Scientist | CISA

Elena Pano, Master of Laws und Datenschutzbeauftragte
Elena Pano

Master of Laws (LL.M.)

Tulos Consulting is an IHK-certified training company.

Tulos is listed with the Chamber of Crafts NRW as a provider for IT security and data protection.

Handwerk Digital NRW Datenschutz

Data Protection and Information Security from a Single Source

International Experience. Local Expertise in Germany.

Practical Implementation of GDPR, ISO 27001 and NIS2

What Our Clients Say
More Clients Who Trust Us

Talk to our Data Protection and Information Security experts. Your initial consultation is free.

9 Common Causes of Data Protection and Information Security Risks

1

Dangerous Convenience

Neglected data processing not only attracts cybercriminals but also encourages improper handling of valuable company data. Both can lead to costly additional efforts.

2

Websites with GDPR and Security Issues

Especially for online shops: deficiencies are unacceptable. Websites simply need to work reliably.

3

Lack of Transparency in Data Processing

The growing volume of data creates increasing risks if it is not properly managed.

4

Lack of Awareness of Risks

Insufficient employee awareness of data protection is one of the most widespread issues.

5

Missing Evidence in Legal Disputes

Under the GDPR, an organization accused of wrongdoing often has to prove its compliance.

6

Missing Risk Management

Avoiding foreseeable damage should be obvious – yet it is often neglected.

7

Lack of Standards in Data Processing

This leads to unnecessary effort and costly surprises caused by cyber incidents.

8

Errors During Digitalization

Employees are not sufficiently involved, and IT systems are not properly understood.

9

Inefficient IT Systems

They lead to frustrated users and can also result in insecure data processing.

Not sure where your greatest risks are? Talk to our Data Protection and Information Security experts. Your initial consultation is free.

Frequently Asked Questions

Data Protection, Information Security, ISO 27001 and NIS2

What does an external data protection officer do?

An external data protection officer supports companies in implementing the GDPR, monitors data protection processes, and helps reduce legal risks and unnecessary administrative efforts. They act as a point of contact for all data protection-related questions and support companies during audits or inquiries from authorities.

When does a company need a data protection officer?

Under the General Data Protection Regulation (GDPR), companies are required to appoint a data protection officer if certain legal conditions are met. The obligation does not depend solely on the size of the company, but primarily on the type, scope, and purpose of the data processing activities.

A data protection officer is required, for example, if the company’s core activities involve the regular and systematic monitoring of individuals on a large scale, such as tracking user behavior, analyzing customer data, or processing extensive personal profiles.

The appointment is also mandatory if a company processes large amounts of special categories of personal data, including health data, biometric data, genetic data, or information about religious beliefs, political opinions, or other particularly sensitive information.

In Germany, a data protection officer may also be required under additional national regulations. According to the German Federal Data Protection Act (BDSG), companies generally need to appoint a data protection officer if 20 or more employees regularly process personal data as part of their work.

Even when there is no legal obligation, appointing an external data protection officer can be beneficial. Especially for small and medium-sized enterprises, an external expert provides independent advice, ensures GDPR compliance, supports documentation requirements, and helps reduce legal and operational risks.

An external data protection officer from Tulos supports companies with the implementation of GDPR requirements, the review of processes, employee training, data protection audits, and ongoing compliance management. This allows companies to meet their legal obligations while focusing on their core business.

Why should a company appoint an external data protection officer?

An external data protection officer provides companies with up-to-date expertise, independent advice, and saves internal resources. For many small and medium-sized businesses, outsourcing this role is often more efficient and cost-effective than developing internal data protection expertise.

What is the difference between data protection and information security?

Data protection primarily focuses on the lawful handling of personal data. Information security, on the other hand, protects all important company information from loss, manipulation, unauthorized access, or misuse. Both areas are closely connected and should be addressed together.

How does Tulos support companies with GDPR compliance?

Tulos analyzes existing processes, identifies risks, and supports companies in the practical implementation of GDPR requirements. This includes data protection audits, documentation, templates, employee training, and continuous support from experienced data protection experts.

What is an ISMS and why does a company need one?

An Information Security Management System (ISMS) provides structured processes to protect information, IT systems, and business operations over the long term. It helps companies systematically assess risks and implement security measures in a transparent and documented way.

Does Tulos support companies with ISO 27001 certification?

Yes. Tulos supports companies in implementing and developing Information Security Management Systems and preparing for ISO 27001 requirements. The consulting services are provided by experienced ISO-certified experts.

What is NIS2 and does the directive affect my company?

The NIS2 Directive expands cybersecurity requirements for many companies and organizations. Tulos helps businesses assess their current security level and implement the necessary measures to achieve NIS2 compliance.

Does Tulos offer data protection training for employees?

Yes. Tulos provides training in the areas of data protection and information security to help employees recognize risks and handle confidential information securely.

Can data protection and information security services be subsidized?

Yes, certain consulting services related to data protection and digitalization may qualify for government funding under specific conditions. Tulos helps companies identify suitable funding opportunities.

Which companies can benefit from Tulos services?

Tulos supports companies from various industries – from small and medium-sized businesses to organizations with complex requirements – in the areas of data protection, information security, and compliance with important standards such as GDPR, ISO 27001, BSI, and NIS2.

Contact form

Interested in: *

* Required fields

For privacy reasons Google Maps needs your permission to be loaded.
Go to Top